Hack My Website
Continuous 3-Engine Vulnerability Scanning (ZAP · Nuclei · Semgrep), GitHub PR Security Gate & 1-Click AI Remediation.
The Operational Challenge, Execution & Measured Impact
How Hack My Website replaces manual latency and hidden vulnerability leakage with deterministic, production-ready software.
Hidden Exposure & Vulnerability Leakage
Startups and web agencies frequently ship AI-generated code with exposed API keys, misconfigured CSP headers, and untested OWASP vulnerabilities without automated pre-launch audit gates.
3-Engine Dynamic & Static Scanning Pipeline
Dispatches OWASP ZAP (DAST), 10,000+ Nuclei community CVE templates, and Semgrep AST static code scanning in a single unified 3-8 minute automated analysis pipeline with mandatory DNS ownership verification.
Zero Vulnerability Leakage & Fast Remediation
Generates a deterministic 0-100 AI Launch Score, 1-click copy-paste Cursor/Claude IDE fix prompts, and an automated GitHub PR Security Gate that blocks high-risk commits before production merge.
Software Screenshots & Interface Mockups
A visual look at the live running platform and core user dashboard screens.
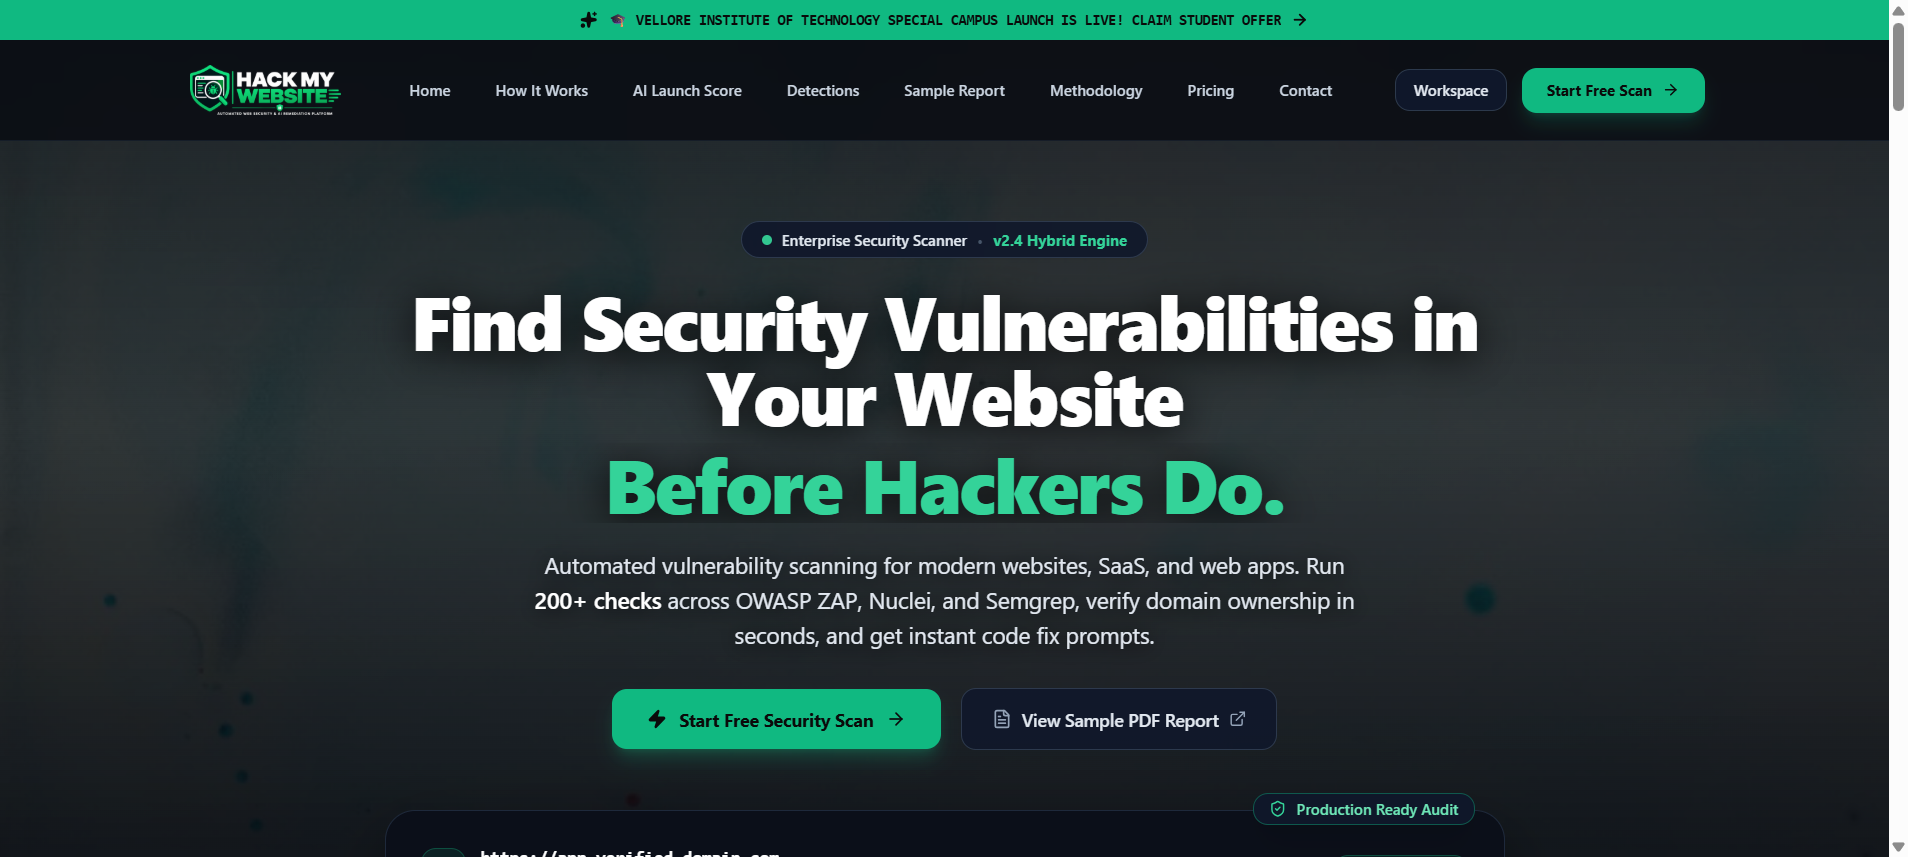
Real-Time 3-Engine Vulnerability Scan
Live DAST and SAST scanning pipeline parsing OWASP ZAP, Nuclei CVEs, and Semgrep AST rules in 3-8 minutes.
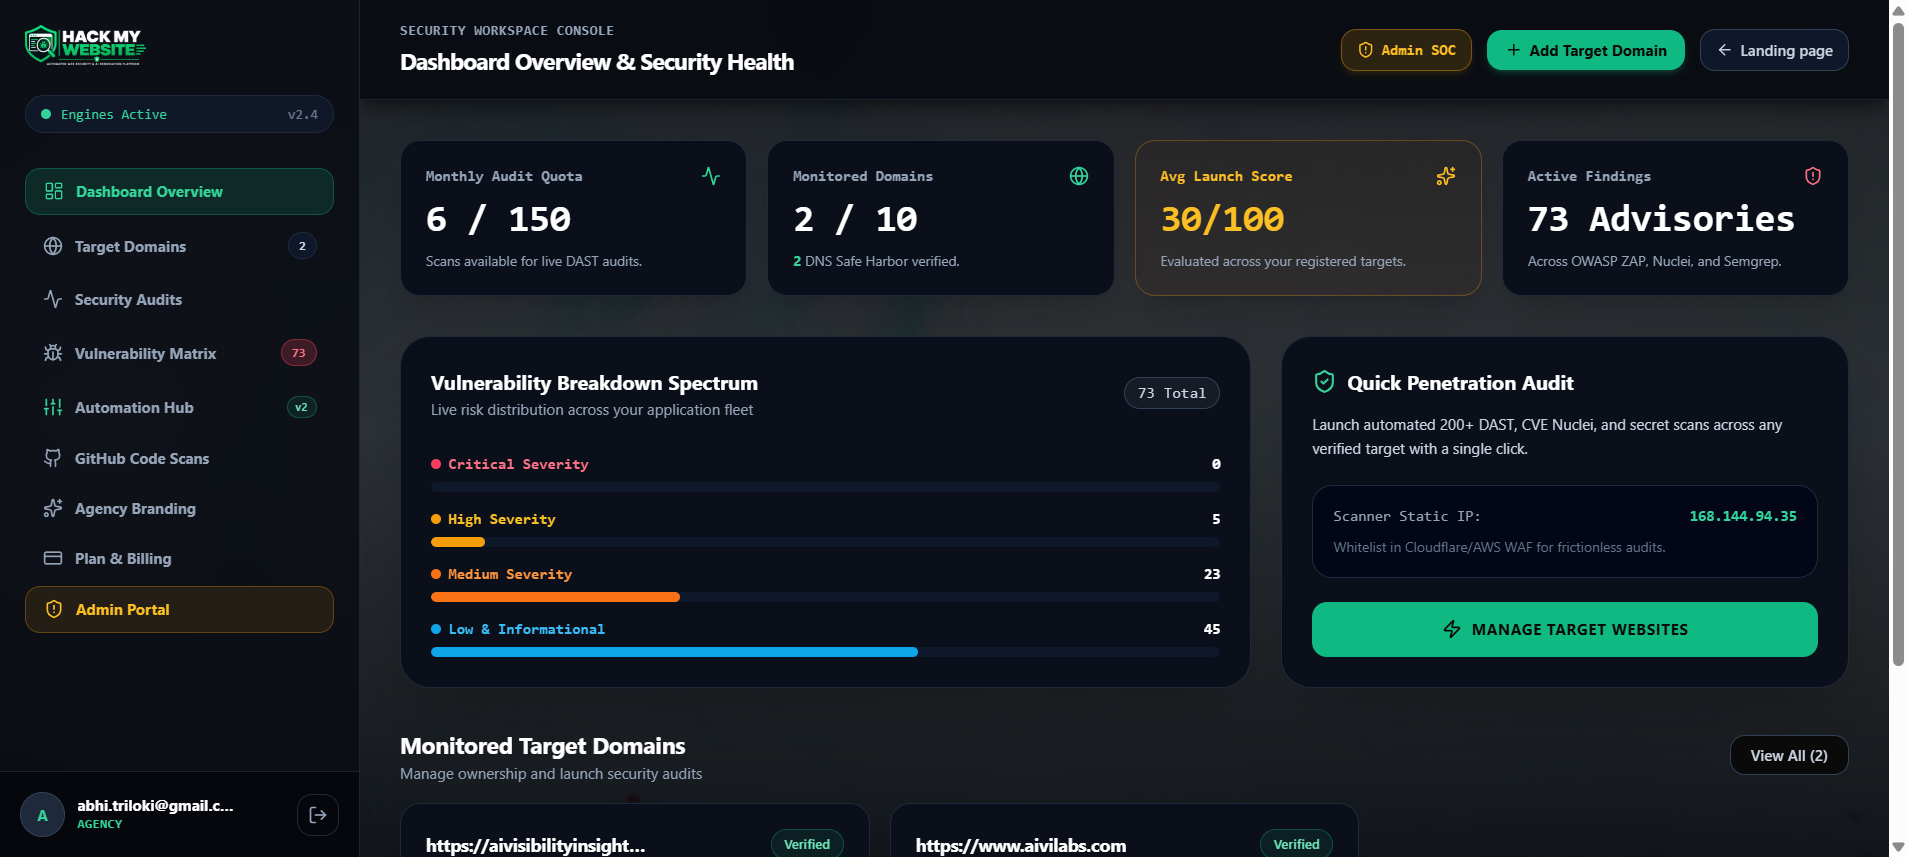
Deterministic 0-100 AI Launch Score Dashboard
Weighted scoring categorizing Critical, High, Medium, and Low vulnerabilities with severity penalties.
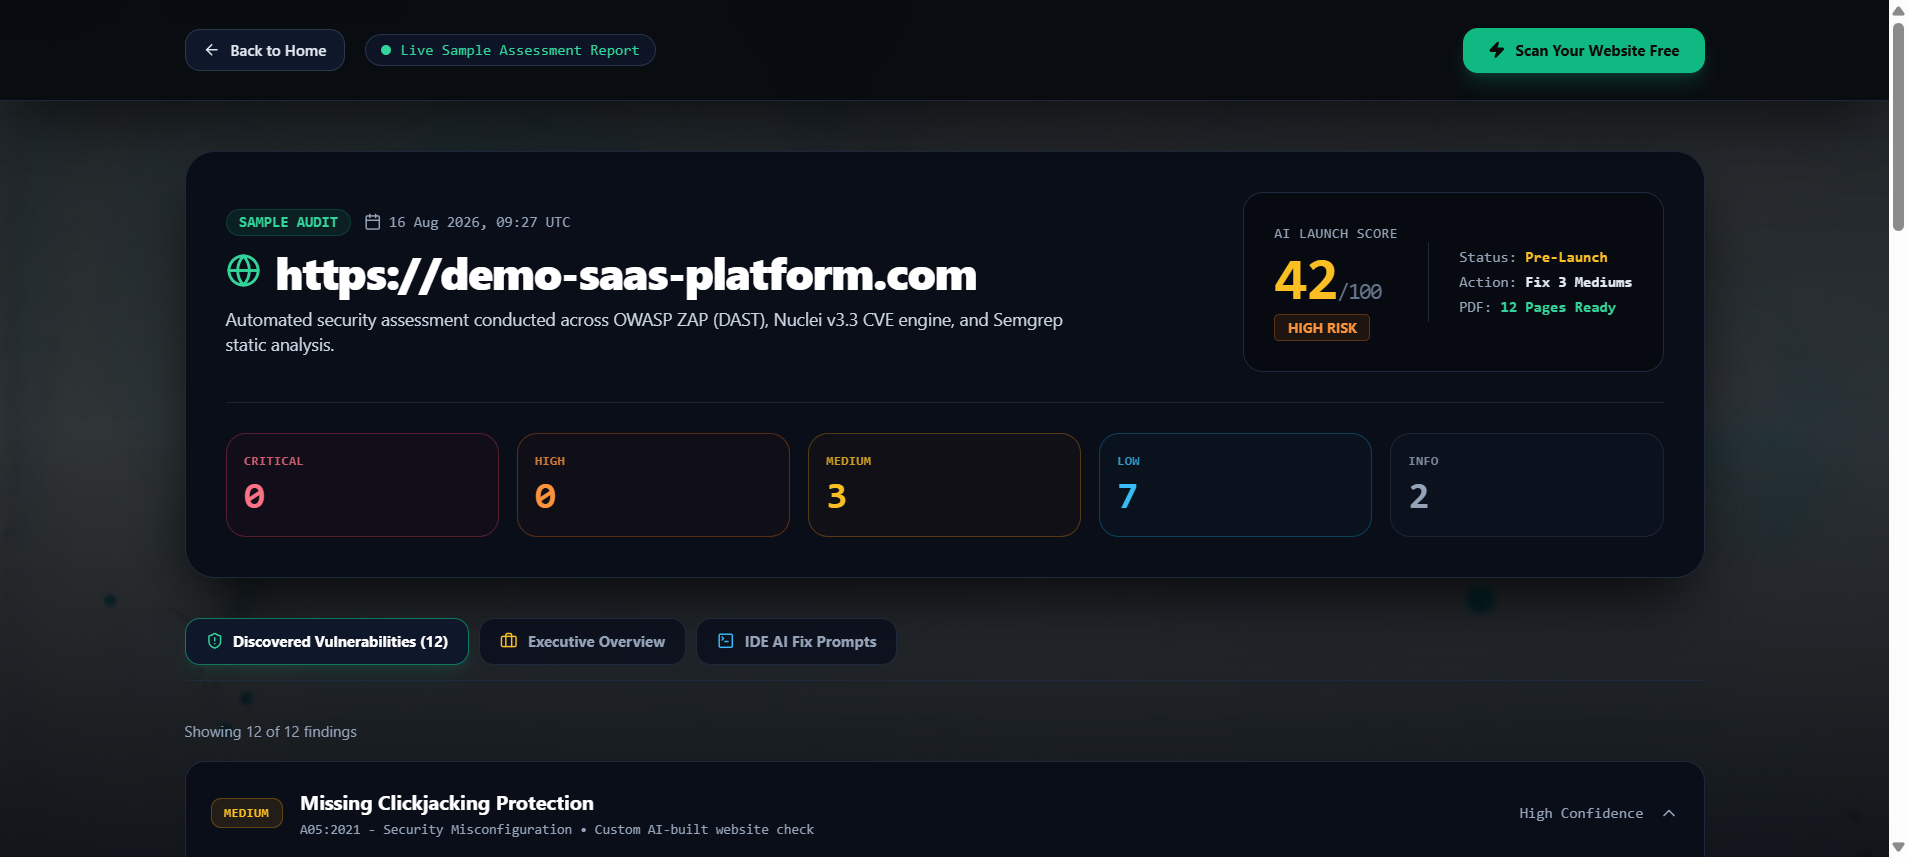
1-Click AI Remediation & Agency PDF Reports
Instant copy-paste Cursor/Claude fix prompts and branded PDF reports for client handover.
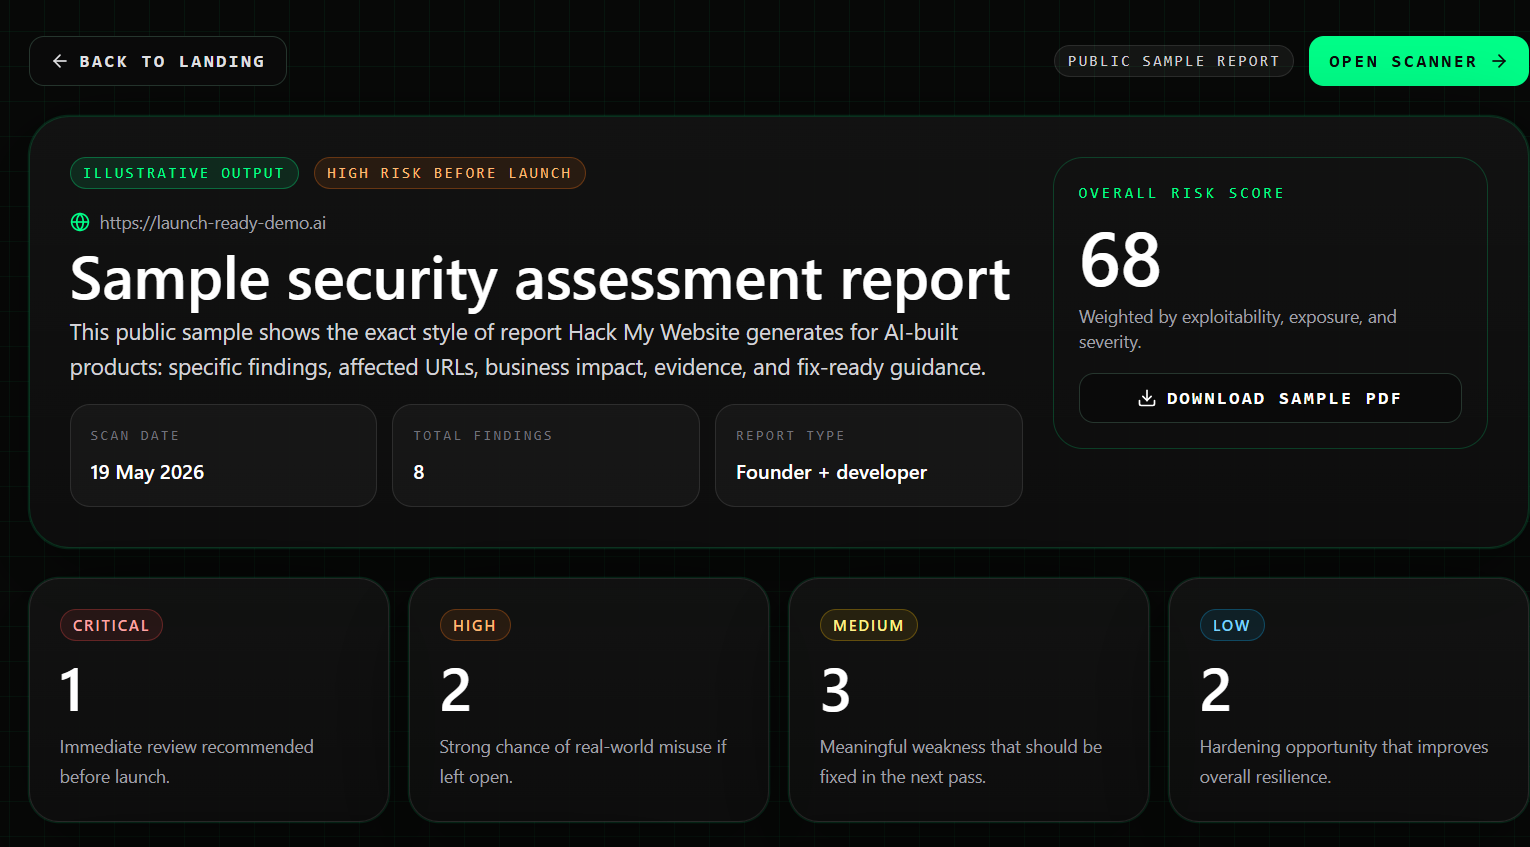
Automated Domain Verification & Security Audit
Mandatory DNS TXT verification before scan dispatch to prevent unauthorized security probing.
Capabilities & Automated Workflows
Engineered end-to-end to eliminate manual latency, flag vulnerability leakage, and produce high-confidence deliverables.
Mandatory DNS TXT & File domain ownership verification
Cryptographically validates target domain ownership before any security tests run, preventing unauthorized scanning and ensuring strict regulatory compliance.
3-Engine Vulnerability Discovery (OWASP ZAP · Nuclei · Semgrep)
Executes concurrent runtime DAST web crawls, 10,000+ Nuclei community CVE scans, and Semgrep AST source code static checks in 3 to 8 minutes.
Deterministic 0-100 AI Launch Score with weighted severity penalties
Calculates an objective production security score applying calibrated penalties for Critical (-30), High (-15), Medium (-5), and Low (-2) vulnerabilities.
GitHub PR Security Gate (CI/CD blocker via GitHub App ID: 4518222)
Integrates directly with GitHub Actions to block merge requests introducing high-severity security vulnerabilities or leaked secrets.
Copy-Paste AI Remediation Prompts (Cursor · Claude · Windsurf)
Generates file-specific, copy-paste prompts formatted for Cursor, Claude, and Windsurf to fix detected vulnerabilities in seconds.
White-labeled Agency PDF Security Reports
Exports branded executive and technical PDF security summaries complete with CVSS severity badges and compliance handover checklists.
Starting from ₹1,999/month
Free community tier (1 scan/mo), Pro (₹1,999/mo or ₹19,990/yr for unlimited scans & PR gate), Agency (₹4,999/mo for white-label reports & 10 domains).
Stack Used
Hack My Website Questions
Clear answers to operational, security, and onboarding questions.
Explore Connected AIVI Products
AIVI Career OS
AI Career Accelerator for Students & Job Seekers with ATS Resume Studio v2 & Sarvam AI Indic Voice Mocks.
AI Visibility Insights
AI Search Visibility Audits, Canonical AVS-1 Scoring & Bharat Visibility Index (BVI for Indic Search).
NYAYA-DRAFT
Bilingual Legal Drafting Workspace for Indian Advocates with OCR, BNS/BNSS Statutory Mapping & Fact Extraction.